TheDPDPAct.com -
Official WhatsApp Channel
Stay updated with the latest DPDP Act news, compliance insights, updates, and resources.
Join Our WhatsApp Channel →Most organizations don't fail DPDP compliance because they ignored the law.
They fail it because compliance looks simpler from the outside than it turns out to be in practice — and the gaps that matter most only become visible once someone is already inside the program, mapping data flows and discovering that a checkbox at registration doesn't satisfy Section 6, or that a written breach response plan has never been tested against the 72-hour notification window that makes it actually useful.
Industry analysis consistently puts the timeline for a complete enterprise DPDP compliance program at nine to twelve months — covering gap assessment, control implementation, and genuine audit readiness. For organizations that haven't yet started, the May 2027 deadline is not the runway it sounds like. And for organizations that have "started" in the form of a privacy policy update and a consent banner, the distance between that starting point and genuine compliance is often larger than anyone in the room has formally assessed.
This piece is about what end-to-end DPDP consulting actually involves — not as a services menu, but as an honest account of where compliance programs typically break down and what it takes to close each gap properly.
Where DPDP Compliance Actually Breaks Down
Understanding why consulting matters starts with understanding where organizations consistently get this wrong on their own.
DPDP compliance rarely fails because organizations ignore the law. It fails because daily operations move faster than governance — personal data spreads across tools, teams, and vendors while compliance remains trapped in policies and intent. The failure points that come up most consistently are predictable enough to be worth naming directly.
1. Data visibility is incomplete.
Many organizations still operate with incomplete data inventories — a gap that becomes considerably harder to manage when personal data sits in unstructured formats like emails, PDFs, logs, and spreadsheets. An organization that doesn't know where all its personal data lives cannot give accurate notice under Section 5, cannot honor an erasure request under Section 12, and cannot assess the scope of a breach accurately enough to notify the Board within 72 hours. Data discovery is the prerequisite for everything else — and it is consistently underestimated in both time and complexity.
2. Consent architecture is weaker than it appears.
A consent checkbox at account creation is not DPDPA-compliant consent. Section 6 requires consent that is specific to each processing purpose, given separately, and withdrawable as easily as it was given — with that withdrawal propagating to every system and processor holding the covered data. Building the consent management infrastructure that actually satisfies this is an engineering project, not a policy drafting exercise, and most organizations haven't built it.
3. Security safeguards are asserted rather than demonstrated.
Section 8(5) carries the Act's highest penalty — INR 250 crore — and requires reasonable security safeguards that can be demonstrated under regulatory scrutiny. Describing security controls in a policy document is not the same as being able to produce penetration test evidence, access control logs, and a tested breach response that meets the 72-hour timeline. The gap between what most organizations can document and what they could demonstrate under a Board investigation is frequently significant.
4. Breach detection and response is untested.
Most enterprises struggle with both detection and coordinated response — insufficient logging makes it difficult to reconstruct breach timelines or identify affected data subjects, and unstructured reporting playbooks produce inconsistencies that raise regulatory risk. A breach response plan that exists only on paper — never run through a simulation, never tested against a realistic incident — is not a compliance asset. It is a document that will fail in the moment it matters most.
5. Vendor governance has gaps nobody has mapped.
A significant share of DPDP compliance failures in 2026 trace back to third-party vendor relationships where personal data moves to processors operating under contracts that were never updated to reflect the DPDPA's requirements. The Data Fiduciary remains accountable for every processor in its chain, which means a vendor's inadequate security practices are the Fiduciary's compliance problem.
What End-to-End DPDP Consulting Actually Covers
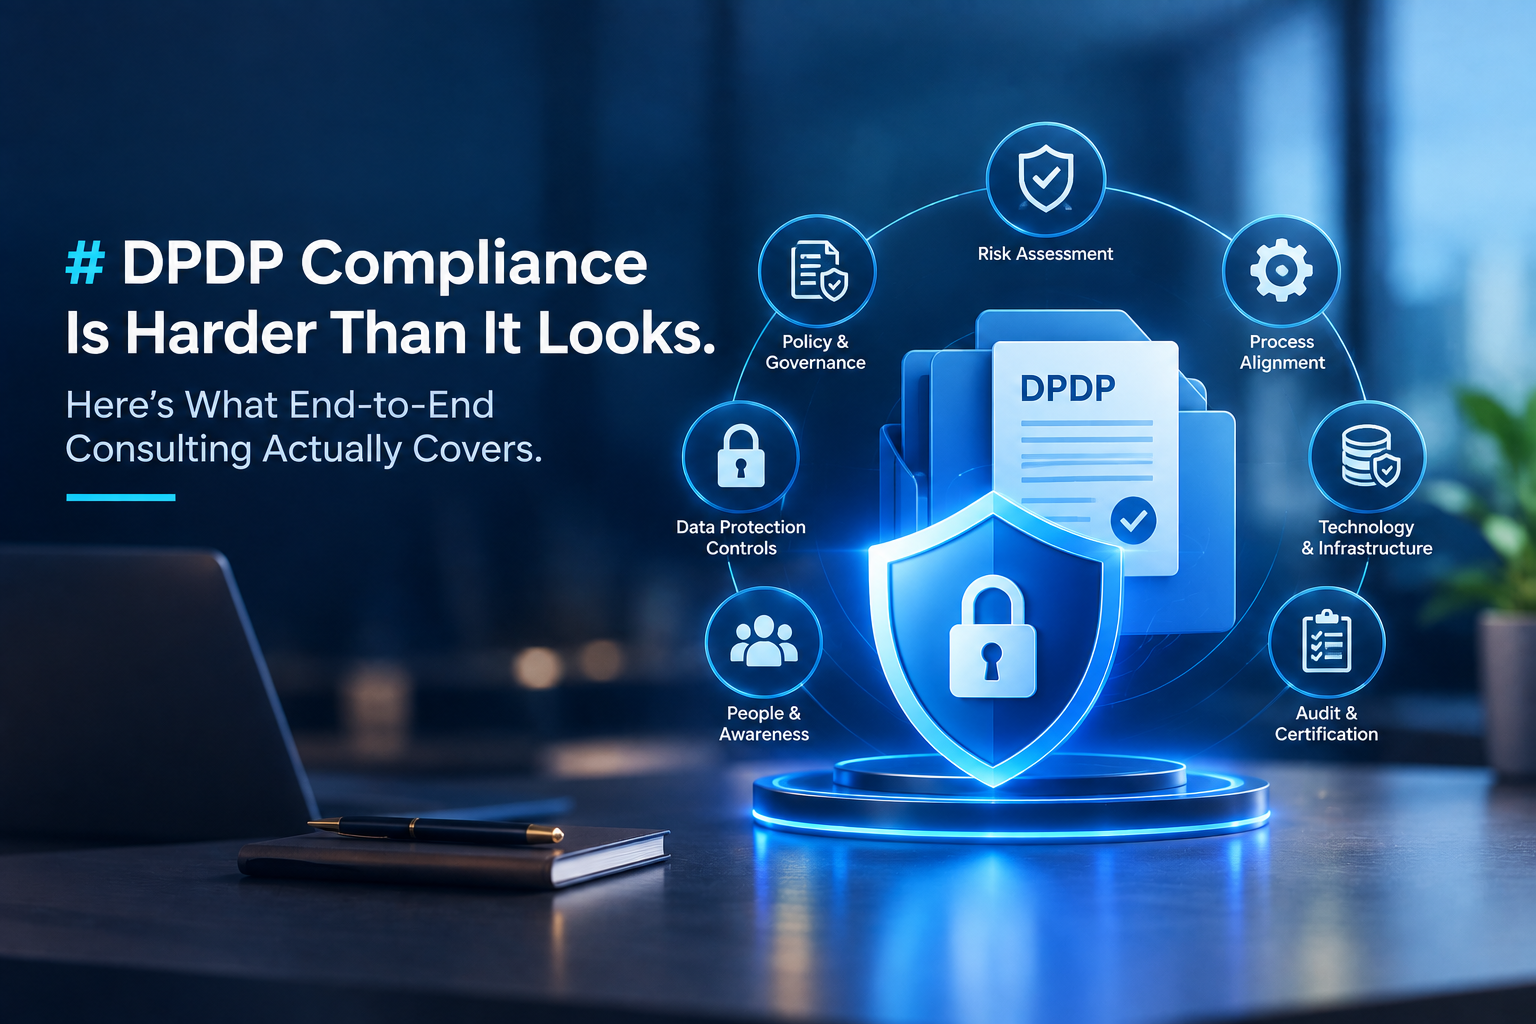
A consulting engagement built around genuine compliance — not just documentation — addresses these failure points systematically rather than leaving them for the organization to discover during a regulatory investigation.
1. Discovery, classification, and mapping.
Before any other compliance work is meaningful, an organization needs an accurate, current picture of what personal data it holds, where it lives, how it flows across systems and vendors, and what purpose justifies its collection. This is painstaking work — it touches every application, every database, every third-party integration — and it almost always surfaces data that nobody formally knew the organization was holding. It is also the work that every subsequent phase of compliance depends on.
2. Gap assessment against the Act's actual requirements.
A gap analysis that compares current practices against the DPDPA's statutory text and the DPDP Rules 2025 — not against a generic privacy framework — produces findings specific enough to turn into a remediation roadmap. This phase identifies not just what's missing, but what's hardest to fix, what's quickest to close, and what the right sequence is for a program operating against a defined deadline.
3. Consent architecture design and implementation.
Designing a consent framework that satisfies Section 6 requires understanding both what the law requires and how the organization's specific products and processing purposes are structured. The implementation is a technical build — consent management infrastructure, purpose-specific flows, withdrawal mechanisms, propagation to downstream processors — that requires engineering involvement alongside legal guidance.
4. Policy development that reflects operations, not aspirations.
Privacy policies, data retention and disposal policies, incident response policies, and grievance redress procedures need to describe what the organization actually does rather than what it intends to do. A privacy policy that describes a consent architecture the organization hasn't built, or a breach response process that hasn't been implemented, doesn't satisfy the Act's requirements — it creates evidence of the gap.
5. Security implementation and technical safeguards.
This is where DPDP consulting overlaps directly with cybersecurity: implementing encryption at the standard the data requires, establishing access controls with proper audit trails, running vulnerability assessments against the systems holding personal data, and building the breach detection capability that makes the 72-hour notification requirement achievable rather than aspirational. Meeting that deadline requires automated detection and internal escalation tools, clear incident response teams, and pre-prepared communication templates for notifying the Board and data principals — none of which can be assembled effectively under the pressure of a live incident.
6. Data principal rights fulfillment.
The right to access, correction, erasure, and grievance redress needs an operational workflow — tested end-to-end, not just described. A consulting engagement builds and validates this workflow, including the organizational assignment of who owns each request type and the technical mechanism for fulfilling it within the expected timeframe.
7. Vendor and third-party governance.
Reviewing significant vendor relationships against DPDPA requirements, updating data processing agreements to include appropriate contractual protections, and implementing a vendor risk assessment process creates the accountability chain the Act requires. It also protects the organization from the compliance exposure that flows from a vendor breach where the contractual framework didn't provide for it.
8. Employee awareness and capability.
Compliance programs built entirely around policy documents without building the human capability to execute them consistently tend to fail at the operational level — the staff member who forwards a customer file to the wrong team, the developer who logs personal data without considering retention, the support agent who doesn't recognize a data principal rights request when they receive one. Training that builds practical understanding, not just policy awareness, is an investment that changes actual behaviour.
9. Audit readiness and ongoing compliance.
Compliance is not a one-time milestone — it requires quarterly internal audits, annual external audits, and ongoing monitoring that keeps pace with how the organization's data processing actually evolves. A consulting engagement that produces a compliance program without building the ongoing governance to maintain it is a program that begins to decay from the day it's delivered.
The Question Worth Asking Before You Start
The most useful question any organization can ask at the beginning of a DPDP compliance program is not "what does the Act require" — the answer to that is knowable. It's "what does our current practice actually look like against those requirements, specifically, for our systems, our data, our vendors, and our processing purposes."
That question almost always produces surprises. The data that's being held without a clear retention end-date. The vendor whose contract predates the DPDPA and contains no data processing obligations. The consent mechanism that was built for marketing purposes and is now being used to cover processing the business never disclosed. The breach response runbook that describes a detection capability the organization doesn't actually have.
Finding these gaps now — through a structured, expert-led assessment — is less expensive, less operationally disruptive, and considerably less reputationally damaging than finding them during a regulatory investigation, a breach response, or an enterprise due diligence process that stalls because the compliance documentation doesn't match what the data flows actually look like.
At ILLUME Intelligence, our DPDP consulting services are built around exactly this: helping organizations understand where they actually stand, building the technical and operational compliance program that closes the gaps, and producing the evidence of reasonable safeguards and documented compliance that the Act ultimately requires. If May 2027 is on your compliance calendar and the gap assessment hasn't been done, that's the right place to start. Reach out to Illume to scope an engagement.