TheDPDPAct.com -
Official WhatsApp Channel
Stay updated with the latest DPDP Act news, compliance insights, updates, and resources.
Join Our WhatsApp Channel →Here's a number worth sitting with: the global average time to identify and contain a breach in 2026 is 247 days. One hundred and eighty-three days to detect it. Sixty-four days to contain it after that. Nearly eight months from the moment an attacker first moves inside your environment to the moment your security team has it under control.
That number, from IBM's Cost of a Data Breach Report 2026, is not a technology problem. Modern organizations have SIEMs, EDRs, firewalls, identity platforms, and SOC teams watching dashboards around the clock. The problem is a detection problem — specifically, the gap between the threats a SOC is configured to detect and the threats actually being used against it.
Understanding that gap is what separates a SOC that generates alerts from a SOC that catches attacks.
The Speed Asymmetry Nobody Talks About Enough
Before examining what SOCs should detect, it's worth understanding the speed at which modern attackers operate — because detection timelines that seemed acceptable five years ago are now structurally inadequate.
CrowdStrike's 2025 research found that the fastest 25% of intrusions reached data theft within 72 minutes of initial access. The fastest recorded lateral movement from initial compromise to the next system: 27 seconds. The median attacker breakout time — the window between gaining initial access and moving beyond the first compromised system — was 29 minutes in 2025.
Twenty-nine minutes. The average SOC analyst hasn't finished triaging the alert in that time.
This asymmetry is the defining operational challenge of modern threat detection. Attackers move faster than alert queues. A SOC that waits for an analyst to review, enrich, and escalate a detection before acting is consistently losing the race against the attacker's clock.
Detection, therefore, is not just about coverage — it's about coverage that produces actionable intelligence fast enough to matter.
What Modern Attackers Actually Do
The second problem with many SOC detection programs is that they were designed for a threat landscape that has materially shifted. Detection rules written for perimeter breaches and malware-based attacks are not well-matched to how most enterprise compromises actually begin and progress today.
The pattern that shows up consistently across 2025 and 2026 incident response data is identity-led intrusion. Attackers obtain valid credentials — through phishing, credential stuffing, purchasing them from initial access brokers, or extracting them from earlier breaches — and log in exactly as designed. No exploit fires. No malware drops. No signature triggers. The attacker simply appears in the environment as a legitimate user.
From there, the campaign is one of patient enumeration: mapping the environment, escalating privileges through legitimate Active Directory features, moving laterally using tools that already exist on the target systems (living-off-the-land binaries), and reaching target data before any individual action has crossed a threshold someone configured as suspicious.
A 2025 analysis found that 67% of security teams lack sufficient visibility into access behaviors and lateral movement — despite 73% of security leaders ranking identity-based threats among their highest priorities. That 13-point gap between threat recognition and detection capability is where most enterprise breaches live.
The Five Detection Categories a Modern SOC Cannot Afford to Miss
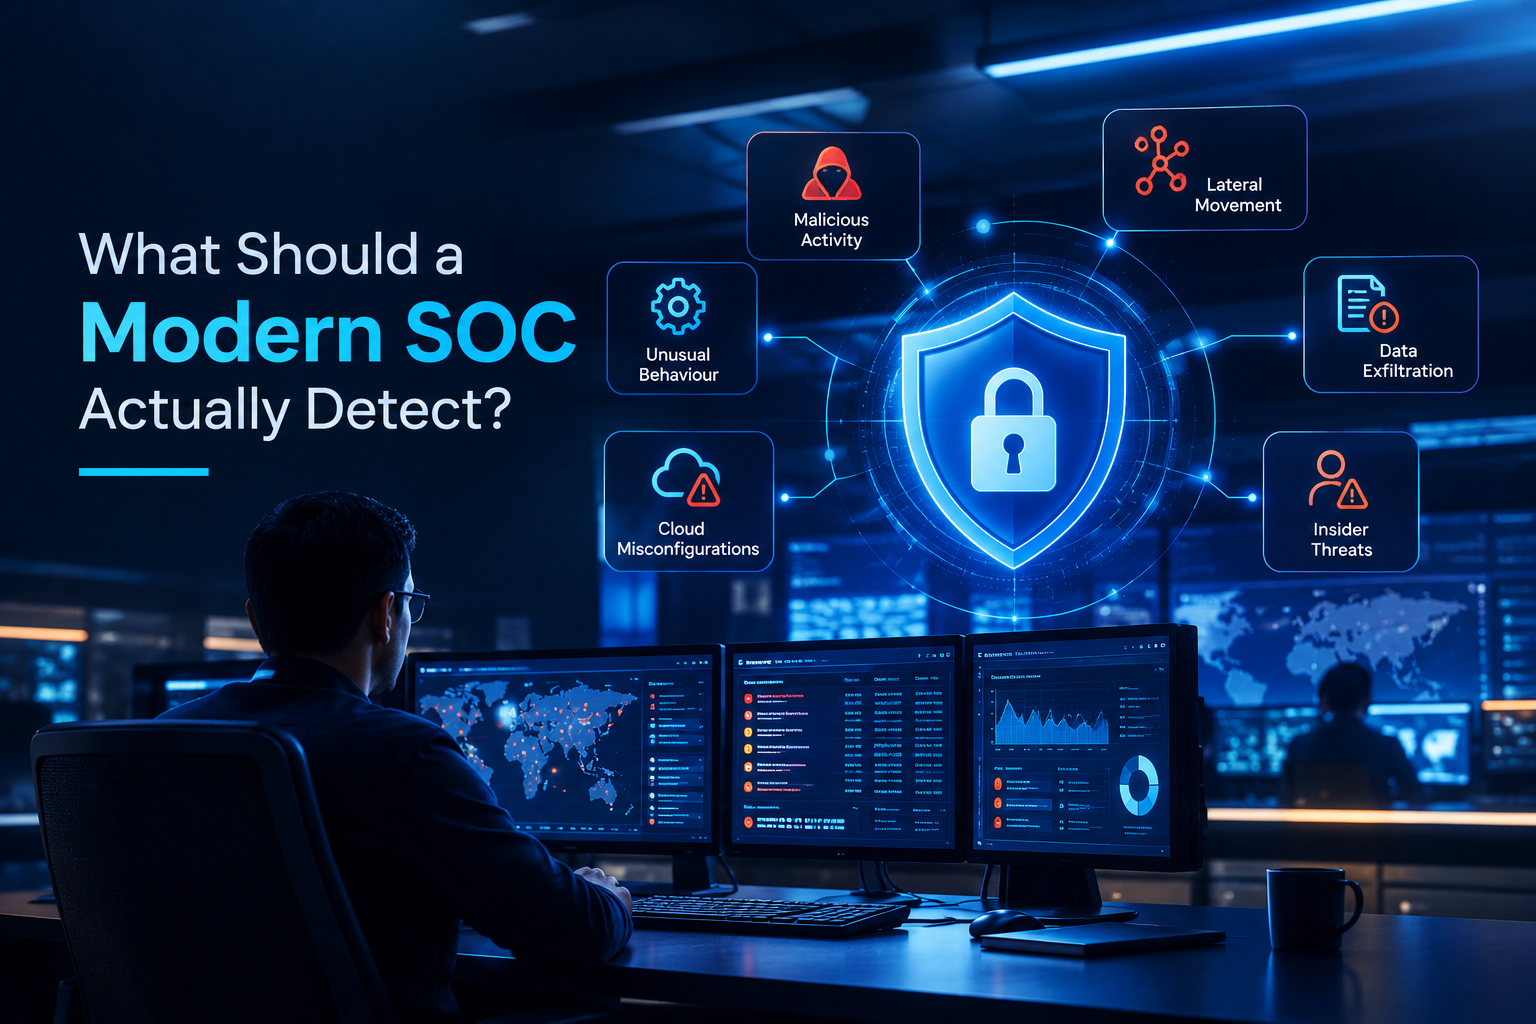
1. Identity Behaviour, Not Just Authentication Events
Authentication events — successful logins, failed logins, MFA prompts — are table stakes. They tell you someone authenticated. They don't tell you whether the authenticated session is behaving the way that user normally behaves.
What effective SOC monitoring adds is behavioural context: Is this user logging in from a location they've never used? At a time inconsistent with their normal pattern? Accessing systems outside their usual scope? Enumerating permissions they've never touched before? Using a protocol their role doesn't typically require?
None of these individual signals necessarily indicates compromise. All of them together, correlated across a session, constitute a behavioural anomaly that warrants investigation — and that a rule looking only for failed authentication events will completely miss.
The core detection challenge with identity-based attacks is that compromised credentials blend into normal activity patterns by design. Detection requires building a baseline of what legitimate looks like for each user and role, and alerting when behaviour diverges from that baseline in ways consistent with post-compromise activity.
2. Lateral Movement Across Domains
Lateral movement is where attackers turn initial access into meaningful compromise — moving from the first foothold to the systems, data, or infrastructure that constitute the real target. It is also the category where SOC detection most consistently fails.
The failure mode is architectural: most SOC monitoring is built around individual tool domains. The EDR monitors endpoints. The SIEM correlates logs. The cloud platform monitors cloud-native behaviour. Each tool sees its own slice of the environment. What none of them does automatically is correlate access sequences that cross domain boundaries — an attacker who compromises a cloud workload, moves to an on-premises endpoint, and then accesses a privileged Active Directory account may be visible in all three domains individually and invisible as a connected campaign in any of them.
Effective lateral movement detection requires cross-domain correlation: the ability to link an anomalous cloud login to a subsequent privileged endpoint session to an unusual Active Directory query and surface that chain as a single, connected alert — not three separate, individually low-priority events.
3. Living-Off-the-Land Technique Execution
The shift away from custom malware toward living-off-the-land techniques — using legitimate operating system tools, scripting engines, and remote management utilities to carry out attack steps — is one of the most significant changes in attacker tradecraft over the last five years. It is also one of the most poorly addressed gaps in enterprise detection.
PowerShell executing encoded commands. WMI being used for remote execution. PsExec moving laterally between hosts. Certutil downloading payloads. RDP being used for persistence. None of these behaviours require custom tooling. All of them appear in every major adversary playbook. And all of them can look, in isolation, like a legitimate administrative action.
Detection here requires context: not just that PowerShell ran, but what it ran, from where, under which user account, at what time, following which other events. This is the difference between a detection rule that fires on every encoded PowerShell execution (too noisy to act on) and one that fires on encoded PowerShell execution by a user account that has never run PowerShell before, immediately following an anomalous authentication event (actionable).
4. Cloud Control Plane Activity
As enterprise infrastructure has moved to the cloud, attackers have followed — and in many organisations, the SOC's detection coverage has not kept pace. Cloud environments introduce attack surfaces that have no direct equivalent in on-premises infrastructure: IAM role manipulation, storage bucket permission changes, new API key creation, Lambda function modification, CloudTrail logging being disabled.
These control plane actions are where cloud attacks operate. An attacker who has obtained cloud credentials isn't moving through the network — they're making API calls that modify the cloud environment itself. They're creating new IAM roles with excessive permissions, disabling logging to reduce their visibility, staging data in storage buckets for exfiltration, or establishing persistence through cloud-native mechanisms that on-premises detection tools simply don't see.
Effective SOC monitoring in cloud environments requires native cloud telemetry feeding into the detection stack — not as a separate security console that the cloud team watches independently, but integrated into the same correlation layer as endpoint and network events.
5. Data Staging and Exfiltration Indicators
By the time data is actively leaving an environment, many SOC programs have already missed the window to prevent meaningful damage. The median time from initial compromise to data theft in 2025 was two days. The fastest cases reached exfiltration within 72 minutes.
Earlier-stage exfiltration indicators — data staging behaviour before transfer begins — are the signals that provide a realistic opportunity to intervene. An account accessing significantly more data than its baseline. Bulk file operations on systems the account doesn't normally touch. Compression utilities running on sensitive file directories. Access to backup systems or data repositories outside normal patterns.
These behaviours precede exfiltration. Detecting them is the detection that actually prevents data loss, as opposed to the detection that confirms it happened.
The Alert Quality Problem
Detection coverage is only half the equation. A SOC that generates ten thousand low-quality alerts per day and misses the three that matter has a detection quality problem, not a coverage problem.
The benchmark for world-class SOC operations is a false positive rate below 10%. Most enterprise SOCs operate significantly above that threshold. Gartner projects that AI will handle approximately half of Tier 1 analyst responsibilities by 2028 — not because the work is simple, but because the volume of alerts exceeds what human analysts can process at the quality level meaningful detection requires. IBM's research found that organisations using AI and automation extensively cut their breach lifecycle by 80 days and saved close to $1.9 million on average compared to those that didn't.
Alert quality — high-fidelity, contextually enriched, accurately prioritised signals — is what converts SOC coverage into SOC effectiveness.
The Question That Matters
The right question for a SOC isn't "do we have monitoring in place." It's "does our monitoring detect the techniques attackers are currently using, fast enough to matter, with the fidelity to produce alerts analysts can act on?"
The 247-day average breach lifecycle suggests most organisations are further from a yes on that question than their dashboard would indicate.