TheDPDPAct.com -
Official WhatsApp Channel
Stay updated with the latest DPDP Act news, compliance insights, updates, and resources.
Join Our WhatsApp Channel →Consider a situation:
On a Tuesday afternoon at a product company in Whitefield.
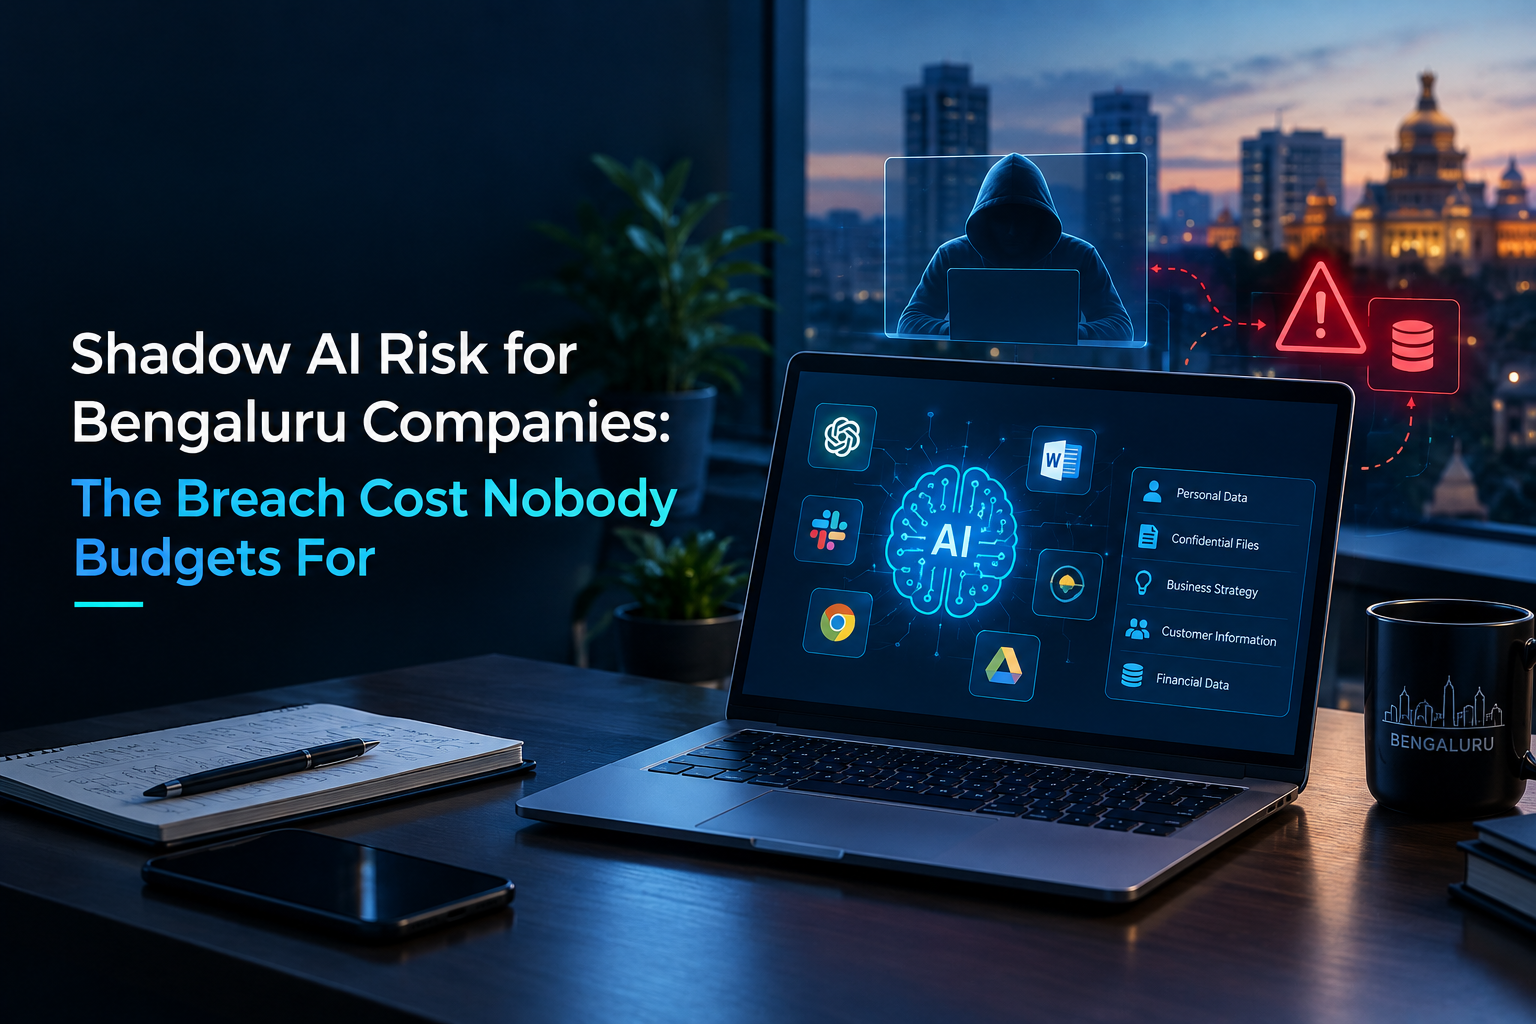
A developer is stuck on a stubborn bug, so she pastes a few hundred lines of proprietary code into a public AI chatbot. A colleague in finance uploads a customer spreadsheet to summarize it. Nobody approves either action, nobody logs it, and nobody thinks of it as a security event. This is a hypothetical scene, but the pattern behind it is measured in real data, and it now shows up on the breach invoice.
In IBM's 2026 Cost of a Data Breach Report, shadow AI is one of the top three factors raising breach costs in India, adding an average of INR 1.79 crore to the bill wherever it is present.
What "Shadow AI" Actually Means
Shadow AI is the use of AI tools by employees without security approval or oversight: a chatbot on a personal account, a browser extension that summarizes documents, an AI notetaker that joins client calls. It is not malicious. It is people trying to work faster. The risk comes from what flows into those tools, and from the fact that security teams cannot protect what they cannot see.
The Numbers Behind the Risk
IBM's 2026 report, based on 602 breached organizations across 16 countries, puts hard figures on the problem:
* Shadow AI was involved in 43% of security incidents at breached organizations, up from 20% a year earlier.
* Those incidents averaged $5.39 million, against a global breach average of $4.99 million.
* About 21% of shadow AI incidents ended in a regulatory fine, a figure IBM measured for the first time this year.
* 68% of breached organizations lacked AI governance to manage AI or detect shadow AI, and only 32% had an AI policy in place.
The control gaps are widening, too. Regular audits for unsanctioned AI fell from 34% to 29% of organizations, and employee training on AI risks slipped from 36% to 30%. Adoption is moving faster than oversight.
India's Exposure Is Sharper Than the Global Average
Netskope Threat Labs' 2026 India report suggests why the local picture matters. It found that 83% of employees in India now use AI tools, up from 55% a year earlier. The average Indian organization recorded more than 3,000 AI-related data policy violations per month, over ten times the global average of 223.
The content leaving the building is revealing. Source code accounted for 49% of the data exposed, followed by regulated data (23%), intellectual property (23%), and passwords and API keys (5%). These figures come from vendor research tracking its own customer base, so read them as a strong indicator rather than a census. Even so, the direction is consistent with IBM's independent findings.
Why This Lands Hardest in Bengaluru?
Bengaluru's economy is built on exactly the assets that leak most easily into AI tools. The city is home to a dense concentration of product companies, SaaS firms, startups, and global capability centers (GCCs). One ANSR analysis counted more than 285 Forbes Global 2000 GCCs based here. That is a lot of engineering teams writing code daily for parent companies whose intellectual property they are responsible for protecting.
If source code is the largest category of exposed data, as suggested in the findings, then an engineering-heavy city carries more of that risk than most. A GCC also faces a second layer of accountability: its own policies, plus the standards its global parent expects. An AI tool that was never approved can put both at risk at once.
That is our inference from the data, not a measured Bengaluru statistic. But the logic holds for any organization where developers hold the crown jewels.
The Counterintuitive Lesson: Blocking Does Not Work, Sanctioning Does
The most useful detail in the Netskope data is a trend. Between the two reporting periods, use of personal AI accounts at work in India fell from 79% to 41%, while use of organization-managed accounts rose from 30% to 77%. Employees did not stop using AI. They moved to approved versions once those existed.
Bans tend to push usage out of sight. Offering a sanctioned, monitored alternative pulls it back into view. Still, 4 in 10 employees continue to use personal accounts, so the job is far from finished.
A Five-Step Playbook
1. Discover what is actually in use. Review network and browser telemetry, SaaS logs, and expense records to build a real inventory, not an assumed one. Expect surprises.
2. Classify the data at risk. Decide which data must never enter an external AI tool: source code, customer personal data, credentials, unreleased financials. Make the rule specific enough to follow.
3. Provide sanctioned tools. Give teams an approved option with enterprise data protections and logging. This is the single step the Indian data suggests moves behavior most.
4. Write a policy people can follow, then train on it. Keep it short, with examples from daily work. IBM's data shows training and approval processes are slipping industry-wide, so this is an easy place to get ahead.
5. Test the controls. Policies on paper are not evidence. AI red teaming checks whether your AI features and guardrails hold up under attack, while an AI governance review shows whether your oversight works in practice.
The DPDP Connection
Shadow AI is not only a security problem. When an employee pastes customer records into an unapproved tool, personal data is being processed outside any controlled process, and the organization remains responsible for it as a data fiduciary. Under India's Digital Personal Data Protection Act, penalties can reach INR 250 crore, with full enforcement due in May 2027. Organizations that can show an AI inventory, a clear policy, and monitoring will be in a far stronger position than those that cannot explain where their data went.
Where ILLUME Intelligence Can Help?
ILLUME Intelligence helps technology and enterprise teams get ahead of this risk through AI Compliance & Governance, which covers AI inventory, policy design, and framework alignment, and AI Red Teaming, which tests whether your AI systems and controls can be manipulated. If your teams are already using AI daily, the first useful step is usually a short discovery exercise to see what is actually running.
Conclusion
Shadow AI is now a measured line item on India's breach invoices, and the gap between AI adoption and AI oversight is widening. For companies in a code-heavy hub like Bengaluru, the exposure is especially concrete. The encouraging finding is that behavior responds to good options: give people sanctioned tools, clear rules, and visibility, and much of the shadow shrinks on its own. Start by finding out what your teams are already using. The answer is rarely what leadership expects.